The Self-Assessment Path Is Open. Finishing Is the Hard Part.
Most CMMC Level 2 self-assessments don't stall on the technology. They stall on the documentation. A finished, accurate self-assessment is the one position that holds whatever comes next.
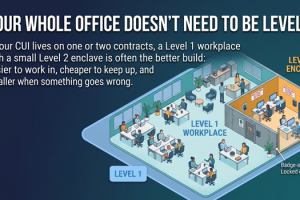
Picture a small defense contractor that handles Controlled Unclassified Information (CUI) on one or two contracts. In the spring, they did almost everything right. They found the clause in their subcontract. They decided to keep CUI in a dedicated enclave instead of dragging the whole company into scope. They bought two laptops that will never touch anything but CUI. Their IT point person worked through the configuration over a few weekends.
Then, somewhere in month two, they opened the System Security Plan (SSP) template.
That is usually where it stops. Nobody decides to stop. The document sits open on a Tuesday night, the cursor blinks next to requirement 3.1.1, and the next contract deliverable wins. Months later the enclave is still configured, the laptops are still CUI-only, and the self-assessment is still unsigned.
If that sounds familiar, you're in good company. Most Level 2 self-assessments don't stall on the technology. They stall on the documentation.
This is Part 3 of The Enclave Build. Part 1 made the case for building a Level 1 workplace with a small Level 2 enclave instead of pulling the whole office into Level 2, and Part 2 showed how a Level 1 company with no CUI yet can use the same design to get ready for CUI work. This part covers why finishing that enclave matters now, and where the project usually stalls, whether it runs on Google Workspace or Microsoft 365 GCC High.
Why Now: What Is in Force Today
Start with what is true this week. The case for finishing rests on obligations already in your contracts, not on anything a task force might recommend later.
Still binding, today
- DFARS 252.204-7012. If it's in your contract, you're obligated to provide adequate security for covered defense information, implement NIST SP 800-171, report cyber incidents within 72 hours, and flow the clause down to your subcontractors. It predates CMMC and does not depend on it.
- NIST SP 800-171. The 110 requirements CMMC Level 2 is built on. Under Secretary Michael Duffey has said on the record that the standards are not being relaxed.
- A current Supplier Performance Risk System (SPRS) score as a condition of award.
- Phase 1 Level 2 self-assessment requirements. Where a contract calls for a CMMC Level 2 self-assessment, that requirement has been in force since November 10, 2025, and the July suspension did not touch it.
- The annual affirmation, signed by a named senior official at your company.
What left in July was the certified third-party assessor organization (C3PAO) requirement. What stayed was the score, the affirmation, and the government's own authority to come look. We covered the mechanics in "Suspended" Is the Wrong Word. So Is "Cancelled.", and the short version still holds: the auditor left, the affirmation didn't. With no assessor standing between your documentation and your signature, the documentation carries the whole weight.
That is why this is an unusually good period to finish. The self-assessment path is open. The path in front of a small Level 2 contractor right now is one they can complete themselves: a documented, defensible self-assessment of a right-sized enclave. No six-figure audit sits at the end of it, and no assessor waitlist sits in front of it.
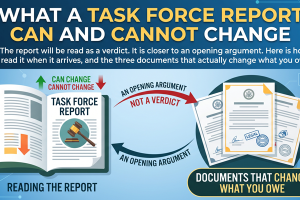
Nobody outside the Department knows what the Task Force will recommend, and this article won't guess. But as we laid out in What a Task Force Report Can and Cannot Change, the obligations listed above don't move when a report publishes. A finished, accurate self-assessment is useful under every outcome. An unfinished one is useful under none of them.
💡 "Now" is about lead time, not a deadline
A Level 2 documentation set is roughly 176 files that have to agree with each other and with your actual configuration. Even done well, that takes calendar time. A contractor who starts now finishes sooner than one who starts after the next announcement. That's the whole argument. No countdown required.
Where Level 2 Actually Stalls
Here is the scale of what a Level 2 self-assessment asks you to document.
The configuration work is real, but it's bounded. A right-sized enclave on a modern cloud platform, with dedicated devices and no Active Directory or SIEM to stand up, is a finite list of settings. People finish it. The documentation is different, for four reasons that compound.
1. It has to describe your enclave, not an enclave
An SSP isn't a policy manual. For each of the 110 requirements, it states how the requirement is met in your environment: which setting, on which system, maintained by which person, checked how often. A template can give you the structure. It can't know that your MFA is enforced through a specific policy, or that your second CUI user works from a home office. Template language that describes a company that isn't yours is the fastest route to an affirmation that doesn't match reality.
That idea, describing what you actually built, is the thread running through Volume 2 of my CMMC Practical Guides, written for the contractor doing the Level 2 documentation themselves. It's also the part that takes the most hours.
2. Everything has to agree with everything else
Your access control policy says accounts are reviewed quarterly. Your procedure says monthly. Your evidence shows one review, in March. Your POAM has to line up with the requirements you scored as not yet met. None of these documents is hard on its own. Keeping 176 of them consistent with each other, and with the configuration, is where rework lives.
3. The person who built it isn't the person writing it
In most small shops, the IT point person configured the enclave and the owner or manager ends up drafting the documents at night. Every requirement turns into a translation exercise: "What did you set for session lock?" "Where's the audit log retention setting?" Those questions are short. The waiting between them is not.
4. Drafting is never urgent on any given day
A contract deliverable is due Friday. A proposal is due Monday. The SSP is due… eventually. Something with no due date loses to everything with one, every single day, until a season has gone by.
The expensive part was never the assessment
For a self-assessment, there's no assessor fee to pay. The real cost is labor and rework: documents drafted, discovered to be inconsistent, and drafted again. The expensive part was never the assessment. It was doing it without a map.
Configured the enclave but stuck at the SSP?
Book a free 30-minute consultation. We'll look at where your build actually stands, what's left between you and a signed self-assessment, and which path gets you there fastest.
Book a Free 30-Minute Consultation →Both Platforms, Same Finish Line
The L2 CUI Enclave Package is built for a dedicated CUI enclave on either Google Workspace or Microsoft 365 GCC High. It's your choice, with platform-specific configuration guides for each. Neither is the right answer for everyone. The better fit depends on what your primes and customers use, what your team already knows, and how CUI reaches you today. Choosing between them is one of the first things we work through on a consultation call.
Google Workspace enclave
- Enclave configuration guides written for Google Workspace's admin settings
- Evidence collected from the Google Workspace Admin console
- An SSP that names your actual Google Workspace settings, not generic "cloud"
Microsoft 365 GCC High enclave
- Enclave configuration guides written for GCC High's admin settings
- Evidence collected from the Microsoft 365 GCC High admin centers
- An SSP that names your actual GCC High settings, not generic "cloud"
What doesn't change between them: the same 110 practices, the same 182 defined artifacts, the same pre-filled SSP structure, POAM framework, Risk Register, and evidence checklist. Either way the enclave is designed for dedicated CUI-only devices (Windows laptops or Chromebooks) and for limited CUI needs: no Active Directory, no SIEM, no enterprise IT department. We provide the templates, configuration guides, and consulting. You implement, and you don't buy hardware from us.
One more constant: Level 2 sits on top of Level 1. A contractor holding CUI also holds Federal Contract Information (FCI), so the Level 1 practices are part of the picture regardless of which platform hosts the enclave.
⚠️ Self-Assessment Programs Only. The L2 CUI Enclave Package is scoped for CMMC Level 2 programs eligible for annual self-assessment. Programs required to use a C3PAO are not in scope.
Guided Documentation: The Same Build, Without the Blank Page
For qualifying self-assessment programs, I've been offering a guided path through the documentation, and it has been getting clients to a signed Level 2 self-assessment with stronger documentation than the template-by-template route. It's now a named tier: L2 CUI Enclave — Guided Documentation, $5,495/year. Here's what it is, in the order that matters.
What stays the same
Everything in the L2 CUI Enclave Package. The same 110 practices mapped to the same 182 defined artifacts. The same platform-specific configuration guides for Google Workspace or Microsoft 365 GCC High. The same pre-filled SSP, POAM framework, Risk Register, and evidence checklist. Your consulting sessions don't go away. And you still sign the affirmation. Nothing about the controls gets shorter, and nothing gets skipped.
What changes: the drafting
Instead of working through 182 artifacts template by template, you answer a structured set of questions about how your enclave is actually configured: your settings, your devices, your roles, your procedures. Your answers become your documentation. Your consulting sessions shift from "let's write this together" to "let's review what you have and get it signed."
Where the truth comes from
This is the part that matters most to a careful buyer, so here it is plainly. There are three roles, and you hold the last one.
Your answers
The structured questions capture your environment as you configured it. Your answers are the source of record.
Our review
Your consultant reviews every document against what you actually built before it goes in your Evidence Locker.
Your signature
You sign the affirmation. Nothing gets attested that we haven't looked at together.
If you're wondering whether that's just boilerplate with extra steps: it's the opposite of boilerplate. Boilerplate is a generic template that describes a company that isn't yours. This describes your configuration because your answers are what it's built from.
The boundary
The tool runs outside your CUI boundary. No connection to your tenant, no access to your systems, and it never touches CUI. Its only inputs are your answers about how your environment is set up. It produces documentation about the enclave. It never operates inside it.
Fit comes first
Before you buy, we confirm this fits your environment. If it doesn't, we'll tell you and point you at the right path. Nobody should end up with documentation describing an environment they haven't built yet.
The short version: you configure the enclave. We guide the build. Drafting stops being the bottleneck. Configuration is still on your clock, and that's where the real time goes.
Our Analysis — not a commitment.
📘 Prefer to do the writing yourself?
Volume 1: CMMC Level 1: the 15 practices, the system description, and the annual affirmation every Level 2 contractor also carries.
Volume 2: CMMC Level 2: the Level 2 practices and documentation, for the contractor building it on their own.
Kindle from $12.99. See the full series →
What to Do This Month
Whichever path you take, these steps move a stalled Level 2 project. None of them requires buying anything.
- Find the clause. Check your contracts and your prime's flow-downs for DFARS 252.204-7012 and for any CMMC Level 2 self-assessment requirement. Your contract, not a vendor, tells you what you owe.
- Confirm what you actually hold. Whether information is CUI is set by your contract and the government's marking, with categories defined in the NARA CUI Registry. If it's unclear, ask your contracting officer or prime in writing and keep the answer.
- Confirm your Level 1 baseline. Level 2 sits on top of it. Our free CMMC Assessment Tool checks all 15 Level 1 practices in under 30 minutes.
- Name your three people. An Owner/Manager who signs policies and makes approval decisions, an IT Point Person who implements and maintains the technical controls, and the CUI User(s) who follow the procedures. In a small business, one person may wear two hats. Write the names down anyway.
- Check the date on your SPRS score. If it doesn't describe your environment as it stands today, that's the first thing to fix.
- Define "done." Done is a signed affirmation, a packaged and date-stamped self-assessment, and dated evidence in a locker. It's not "mostly configured." Put that definition where the whole team can see it.
⚠️ Self-Assessment Programs Only. The L2 CUI Enclave Package is scoped for CMMC Level 2 programs eligible for annual self-assessment. Programs required to use a C3PAO are not in scope.
Ready to see the questions?
A free 30-minute consultation walks you through the intake, your platform choice, and whether the guided tier is the right fit for your CUI footprint.
Schedule Your Free 30 Minutes →Coming Up in The Enclave Build
- Part 4: Same Practices, Same Artifacts, Same Signature. A full look at the guided tier: what stays fixed, what moves off your desk, and why the review gate is the point.
- Part 5: Building a Level 2 CUI Enclave, Start to Signature. One enclave, walked phase by phase, with Google Workspace and Microsoft 365 GCC High side by side.
- Part 6: We'll Tell You If It Isn't the Right Fit. Who the guided tier is for, who it isn't for, and where those contractors should go instead.
Sources & Further Reading
- DFARS 252.204-7012: Safeguarding Covered Defense Information and Cyber Incident Reporting
- NIST SP 800-171 Rev. 2
- 32 CFR Part 170: Cybersecurity Maturity Model Certification (CMMC) Program
- DoD CIO: About CMMC
- U.S. Department of War: Department of War Suspends CMMC Phase II Requirements (July 13, 2026)
- Class Deviation 2026-O0025, Revision 3 (September 3, 2026)
- NARA CUI Registry: Category List
This article is general information, not legal advice. Whether your contracts require a Level 2 self-assessment, and whether information you hold is CUI, is determined by your contract and your contracting officer or prime. Questions of contract interpretation should go to your attorney.