The CMMC Pause Didn't Touch Your Civilian Contracts
On July 13 the Department of War suspended CMMC Phase II. Eighteen days earlier, the FAR Council had proposed a governmentwide CUI rule that reaches contractors CMMC never did. One of those two things stopped. The other did not.
By Rob Maupin, founder of Overwatch Tools and author of the CMMC Practical Guides series — Volume 1: CMMC Level 1 and Volume 2: CMMC Level 2.
Since July 13, the conversation among small defense contractors has been almost entirely about one thing: the Department of War suspended CMMC Phase II, the third-party assessment requirement scheduled to land November 10, 2026. We covered what that suspension did and didn't do in a piece the day after it happened.
What got almost no attention in the small-contractor world is what the Federal Acquisition Regulatory Council had done eighteen days earlier.
On June 23, 2026, as part of the Revolutionary FAR Overhaul, the FAR Council published a substantially rewritten proposed rule governing how contractors protect Controlled Unclassified Information (CUI) — not just for the Department of War, but for every civilian agency in the federal government. It replaced a standalone version issued in January 2025, and its comment window closed July 23.
The Department of War paused one verification mechanism inside its own program. The FAR Council kept building an obligation that applies across the whole government. If those two facts have blurred together in your inbox, you're not alone — and if you hold work on both sides, the blur is expensive.
One Pause, Two Regimes
The cleanest way to hold this is to stop treating "CMMC" as a synonym for "federal cybersecurity requirements." CMMC is a Department of War program with its own rule, phase schedule, and — since July — a review underway. The FAR is the acquisition regulation governing contracting across the entire federal government, and it has its own separate track for CUI.
❌ Paused in July
- CMMC Phase II — the November 10, 2026 transition to third-party assessment as a condition of award
- Phases III and IV and future CMMC implementation milestones
- C3PAO certification as a prerequisite for applicable Department of War contracts involving CUI
✅ Never Paused
- The FAR CUI rule — proposed June 23, 2026, comments closed July 23
- CMMC Phase I — Level 1 and Level 2 self-assessment requirements still appear in solicitations
- DFARS 252.204-7012 — the safeguarding and cyber incident reporting clause is fully intact
- NIST SP 800-171 — the underlying standard was never the thing that was suspended
Read the right column again. Every item in it is live today. The suspension covered a verification step in one department's program — not the obligation to protect federal information, and not the separate governmentwide rulemaking that has been grinding forward since 2010.
What the Proposed Rule Would Actually Require
The June 2026 version is not a light edit of the January 2025 proposal. It moved house, changed clause numbers, raised the baseline standard, and rewrote the incident reporting timeline. Here are the pieces that matter most to a small contractor.
A new home in FAR Part 40
The January 2025 version put CUI requirements in FAR Part 4. The June 2026 version relocates them into an expanded FAR Part 40, Information Security and Supply Chain Security. Practically, that puts CUI obligations in the same neighborhood as the Section 889 telecommunications restrictions and supply chain security rules — one place to look instead of four.
The SF XXX — the agency tells you what you're holding
This is the structural change most worth understanding, and it's genuinely good news for small contractors. The proposed rule carries forward a standardized form — designated SF XXX in the draft — that the contracting officer completes for every solicitation and contract. It identifies whether CUI will be involved in performance, which categories are at issue, where the CUI will reside, and which safeguarding and reporting requirements apply.
If you've ever spent a week trying to work out whether a deliverable was CUI or just sensitive, you understand why that matters. The proposal shifts the first move of identification onto the agency rather than leaving contractors to guess. It doesn't eliminate your judgment entirely — the draft still expects contractors to notify the contracting officer when CUI arrives improperly marked — but it changes the starting position.
New clauses: FAR 52.240-6 and 52.240-7
Where CUI is involved in performance, contracting officers would include FAR 52.240-7, carrying the substantive safeguarding and incident-reporting requirements. The June version also drops a January 2025 clause that would have imposed obligations in contracts where no CUI was identified but might turn up anyway — a direct response to contractor complaints about open-ended obligations.
72-hour incident reporting
The January 2025 draft required reporting a suspected CUI incident within eight hours. Commenters pushed back hard, and the June 2026 version revises it to 72 hours, which aligns with the timeline under DFARS 252.204-7012 and the Cyber Incident Reporting for Critical Infrastructure Act. The draft also allows an initial report with whatever data you have, followed by supplemental reports once the investigation is substantially complete.
For a shop without a security operations center, the difference between eight hours and 72 hours is the difference between a requirement you cannot meet and one you can — if you've written the procedure in advance and know who makes the call.
NIST SP 800-171 Rev. 3 as the baseline
Both versions require contractors whose SF XXX identifies CUI to implement NIST SP 800-171. The June 2026 version raises that to Rev. 3. A limited set of contractors handling CUI tied to critical programs or high-value assets could also face the enhanced requirements of NIST SP 800-172.
If the rule finalizes as written, contractors already built to Rev. 2 — which is to say, essentially every defense contractor with a mature DFARS 252.204-7012 program — will need to work the delta between the two revisions. That's the subject of Part 3 in this series, and it's the piece with the longest lead time, which is why it's worth starting before a final rule exists.
Flow-down through every subcontract tier
Prime contractors would flow CUI requirements down through all subcontract tiers where a subcontractor handles CUI, preparing and distributing an SF XXX downstream. The mechanism mirrors the flow-down model under DFARS 252.204-7012. The FAR Council's own estimate is that roughly 7,560 subcontractors per year would be pulled into these requirements.
That number is the one to sit with if you're a subcontractor who has never held a prime contract and has assumed none of this reaches you.
Commercial contracts are not exempt
The clauses would apply to contracts for commercial products and services, with a narrow exception for contracts solely for commercially available off-the-shelf items. Commercial status is not a shield here.
Who This Actually Reaches
Sort yourself into one of three groups.
| Your portfolio | What July 13 changed for you | What the FAR CUI rule would add |
|---|---|---|
| Department of War only | Third-party assessment paused. Phase I self-assessment, DFARS 252.204-7012, and NIST SP 800-171 all still apply. | Nothing directly — but the Rev. 3 baseline signals where the wider federal standard is heading. |
| Civilian agencies only (GSA, VA, DHS, and others) | Nothing. CMMC was never your program. | A first-time, FAR-level CUI safeguarding obligation where you previously faced a patchwork of agency-specific requirements. |
| Mixed portfolio | Relief on the defense side's assessment step only. | A second regime on the civilian side, with its own clauses, its own form, and a higher baseline revision. |
The mixed-portfolio contractor is the one most likely to have misread July 13 as general relief. It wasn't. It was department-specific relief on one mechanism, arriving in the same summer that the civilian side moved toward requirements it had never carried before.
The identification problem comes first
Before any of this becomes actionable, you have to answer a question most small contractors have never had to answer on the civilian side: do I hold CUI at all, or just Federal Contract Information? That distinction drives everything downstream — scope, cost, and which requirements attach. It's the whole subject of Part 2 in this series, and it gets a full treatment in both volumes of the CMMC Practical Guides, because getting it wrong is the most expensive mistake available at either level.
📘 The two-volume reference behind this series
Everything in this article assumes you can tell FCI from CUI, scope a boundary, and recognize when a requirement is finite versus when your scope is negotiable. Those are the two volumes' subject matter.
- CMMC Level 1: A Practical Guide for Small to Medium GovCon Contractors — all fifteen Level 1 practices, the evidence behind each, the system description, and the annual affirmation. Volume 1 on Amazon →
- CMMC Level 2: A Practical Guide for Small to Medium GovCon Contractors — the 110 practices across 14 domains, enclave scoping, and what a defensible Level 2 posture actually looks like at small scale. Volume 2 on Amazon →
Both available in Kindle, paperback, and hardcover — Kindle from $12.99. See the series →
The Head Start Defense Contractors Already Have
Here's the part that reframes this from burden into advantage: contractors with mature DFARS 252.204-7012 compliance programs have a meaningful head start on the FAR CUI requirements. Same safeguarding family, matching incident timeline, familiar flow-down model. What doesn't transfer automatically is the civilian-specific machinery — the SF XXX, the Part 40 structure, and the Rev. 3 delta.
Which produces an unusual situation. The work you did for the defense side, during the period when the defense side's assessment requirement is paused, is the same work that positions you for a civilian requirement that never paused at all. If you wanted a reason to keep momentum through the quiet period, that's a better one than any deadline.
Start With Where You Actually Stand
Our free CMMC assessment tool walks all 15 Level 1 practices, produces an instant gap report and a prioritized remediation roadmap, and flags whether Level 2 may apply to you. Under 30 minutes. No credit card.
Run the Free Assessment →What This Doesn't Mean
Three things, stated plainly, because the alternative is contributing to exactly the noise this article is trying to cut through.
⚠️ This is a proposed rule, not a final one
Nothing described above binds anyone today. Obligations attach when a final rule issues and the clauses appear in your contracts — not before. Proposed language routinely changes between draft and final; the eight-hour reporting window becoming 72 hours is proof of exactly that. Anyone telling you that you are currently out of compliance with the FAR CUI rule is selling something.
Second: nothing here is a forecast of the CMMC Reform Task Force's findings, which are expected roughly mid-September. We'll cover them once they exist.
Third: this is not a reason to panic-buy anything. The FAR Council has said it expects to finalize the Overhaul rules, including the CUI requirements, before the end of 2026 — and that once finalized and inserted into contracts, there would be no phase-in period. That's the fact worth planning around. Not urgency; lead time. The work takes months whether you start it in September or in December, and only one of those is on your schedule rather than a contracting officer's.
What to Do in the Next 30 Days
Inventory your civilian work for CUI exposure
Pull your active civilian-agency contracts and your near-term pipeline. For each, ask whether performance involves information the agency would likely designate as CUI. You're not making a legal determination — you're building a list of contracts to watch when the final rule lands and the SF XXX starts appearing in solicitations.
Treat your defense-side documentation as reusable, not disposable
If you have a system description, artifacts, and evidence built for the defense side, that material is the raw input for a civilian-side posture — not a parallel effort. Contractors who scrapped their compliance work after July 13 are the ones who will rebuild it twice.
Make the scope decision before the requirement forces it
Whole-company or dedicated enclave? That decision drives cost more than any other single choice, and it's much cheaper to make deliberately in September than reactively when a clause shows up in an award. Part 4 of this series works through it in detail.
Watch the right signals
For the FAR side: publication of a final rule and the clauses appearing in solicitations. For the CMMC side: a class deviation, a DFARS rule change, or an amendment to 32 CFR Part 170 — those are the mechanisms that constitute real regulatory change. A memo changes discretion; a rule changes obligations.
Where a CUI Enclave Fits
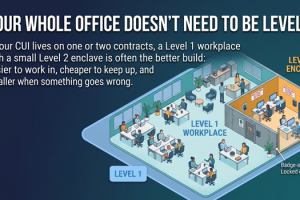
We build enclaves rather than hardening entire companies because the requirement attaches to where the CUI lives. Narrow the boundary and you narrow everything downstream — practices in scope, artifacts, evidence, ongoing maintenance. That logic doesn't change when a second regime shows up: a dedicated enclave is one environment answering to whichever requirements attach to it. What changes is the control revision and the clause set — not the architecture.
Two things are worth being precise about, because the market is not. Level 2 always sits on top of Level 1, not instead of it. The enclave holds CUI; your main business environment still holds Federal Contract Information (FCI) and still carries its own Level 1 obligation — fifteen practices, a system description, a self-assessment scored MET or NOT MET, and an annual affirmation. That's why the two packages are a stack rather than a menu.
And the division of labor is fixed: we provide the templates, the configuration guides, and the consulting sessions. You implement. The L2 CUI Enclave Package maps 110 practices across 14 domains to 182 defined artifacts, with a pre-filled System Security Plan, a POAM framework, a Risk Register, an evidence checklist, and dedicated enclave configuration guides for Google Workspace or Microsoft 365 GCC High. No Active Directory, no SIEM, no full-time security staff, and time estimates on every task so it stays implementable part-time.
The stack, priced
- Free CMMC Assessment Tool — 15 Level 1 practices, instant gap report, under 30 minutes
- L1 Turnkey Package — $2,495/year (limited time, save $500 off the regular $2,995). 8 bi-weekly consulting sessions · 15 practices mapped to 142 artifacts · Microsoft 365 or Google Workspace templates · 8 device and network configuration guides · Evidence Locker · date-stamped self-assessment documentation. Most clients complete in 2–4 weeks, varying with existing infrastructure and responsiveness.
- L2 CUI Enclave Package — $3,495/year. 12 bi-weekly consulting sessions · 110 practices mapped to 182 artifacts.
- Combined L1 + L2 — $5,990/year. The full stack: Federal Contract Information in the main environment, CUI in the enclave.
Not Sure Which Side of the Line You're On?
Thirty minutes, no cost, no obligation. Bring your contract portfolio and we'll work through what you're actually holding and where the boundary should sit.
Book a Free Consultation → See the PackagesThe Second Front — a four-part series
- The CMMC pause didn't touch your civilian contracts (you are here)
- Do you actually hold CUI on a civilian contract? Identification and scoping under the SF XXX
- Rev. 2 to Rev. 3: what changes for a small enclave, and why lead time matters
- One enclave, two regimes: scoping a boundary that answers to both
About the author
Rob Maupin is the founder of Overwatch Tools, a CMMC compliance practice for small to medium defense contractors, and the author of the CMMC Practical Guides series — CMMC Level 1: A Practical Guide for Small to Medium GovCon Contractors and CMMC Level 2: A Practical Guide for Small to Medium GovCon Contractors, both from Overwatch Press. He works with 5- to 50-employee GovCon firms on right-sized compliance.
A guided documentation path for the L2 CUI Enclave Package is in development.
Sources
- Federal Register — Federal Acquisition Regulation: Revolutionary Federal Acquisition Regulation Overhaul, published June 23, 2026 (91 FR 37550): federalregister.gov
- Federal Register — Federal Acquisition Regulation: Controlled Unclassified Information, January 15, 2025 (90 FR 4278, FAR Case 2017-016): federalregister.gov
- Hunton Andrews Kurth — FAR Council Releases Updated CUI Proposed Rule as Part of the Revolutionary FAR Overhaul, June 30, 2026: hunton.com
- Department of War release on the suspension of CMMC Phase II requirements: war.gov
- SBA Office of Advocacy — DoW Requests Information for CMMC Reform Task Force, July 20, 2026: advocacy.sba.gov
- NIST SP 800-171: csrc.nist.gov
This article is general information about a proposed regulation, not legal advice. Contract interpretation and any question touching False Claims Act exposure should go to your attorney.